0 ratings


منتج #:
195806243
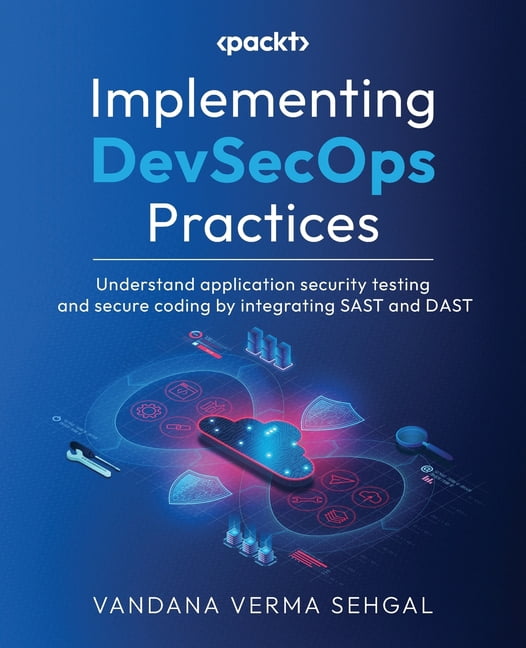
Implementing DevSecOps Practices: Understand application security testing and secure coding by integrating SAST and DAST, (Paperback)
منتج #:
195806243
IQD 75892
تفاصيل السعر
باستثناء رسوم الشحن والجمارك ( سيتم احتساب رسوم الشحن والجمارك عند إتمام الشراء )
*سيتم استيراد جميع العناصر من أمريكا
0 ratings
اكتب رأيك
متوفر فى المخزون
 مستورد من متجر USA
كمية:
بقي1 عنصر فقط في المخزن.
اطلب الآن واحصل عليه حول الأربعاء, أكتوبر 21
معاملة آمنة
تعمل يوباي جاهدة لحماية أمنك وخصوصيتك. يضمن نظام أمان الدفع المتقدم لدينا السرية من خلال تشفير معلوماتك أثناء النقل باستخدام بروتوكولات AES (معايير التشفير المتقدمة) وSSL (طبقة المنافذ الآمنة). تفاصيل الدفع الخاصة بك آمنة بنسبة %100 لأننا لا نشارك تفاصيل الدفع الخاصة بك مع بائعين تابعين لجهات خارجية
أفضل شركائنا اللوجستيين


By the end of this book, you'll know how to apply application security, safe coding, and DevSecOps practices in your development pipeline to create robust security protocols.

شحن
سريع

استرجاع
مجاني*

تغليف آمن

منتجات أصلية %100

الامتثال لمعيار PCI DSS

حاصل على شهادة ISO 27001
Note: Step Down Voltage Transformer required for using electronics products of أمريكا store (110-120). Recommended power converters اشتري الآن.


أبرز ما يلفت الانتباه
Comprehensive Approach
Offers a holistic understanding of DevSecOps by integrating both SAST and DAST methodologies, ensuring a secure coding environment throughout the software development lifecycle.
Practical Guidelines
Provides actionable insights and real-world examples, making complex application security concepts accessible to developers and security professionals alike, enhancing their ability to implement security practices effectively.
Expert Author Insights
Authored by industry experts, this book delivers authoritative knowledge and best practices, ensuring readers obtain reliable guidance for implementing robust application security testing strategies.
تفاصيل المنتج
- Integrate Shift-Left Security, automation, IaC, and compliance into every stage of development, ensuring strong application security and continuous protection for modern software with DevSecOps best practicesKey Features- Understand security posture management to maintain a resilient operational environment- Master DevOps security and blend it with software engineering to create robust security protocols- Adopt the left-shift approach to integrate early-stage security in DevSecOps- Purchase of the print or Kindle book includes a free PDF eBookBook DescriptionDevSecOps is built on the idea that everyone is responsible for security, with the goal of safely distributing security decisions at speed and scale to those who hold the highest level of context. This practice of integrating security into every stage of the development process helps improve both the security and overall quality of the software. This book will help you get to grips with DevSecOps and show you how to implement it, starting with a brief introduction to DevOps, DevSecOps, and their underlying principles.After understanding the principles, you'll dig deeper into different topics concerning application security and secure coding before learning about the secure development lifecycle and how to perform threat modeling properly. You'll also explore a range of tools available for these tasks, as well as best practices for developing secure code and embedding security and policy into your application. Finally, you'll look at automation and infrastructure security with a focus on continuous security testing, infrastructure as code (IaC), protecting DevOps tools, and learning about the software supply chain.By the end of this book, you'll know how to apply application security, safe coding, and DevSecOps practices in your development pipeline to create robust security protocols.What you will learn- Find out how DevSecOps unifies security and DevOps, bridging a significant cybersecurity gap- Discover how CI/CD pipelines can incorporate security checks for automatic vulnerability detection- Understand why threat modeling is indispensable for early vulnerability identification and action- Explore chaos engineering tests to monitor how systems perform in chaotic security scenarios- Find out how SAST pre-checks code and how DAST finds live-app vulnerabilities during runtime- Perform real-time monitoring via observability and its criticality for security managementWho this book is forThis book is for individuals new to DevSecOps and want to implement its practices successfully and efficiently. DevSecOps Engineers, Application Security Engineers, Developers, Pentesters, and Security Analysts will find plenty of useful information in this book. Prior knowledge of the software development process and programming logic is beneficial, but not mandatory.Table of Contents- Introducing DevSecOps- DevSecOps Principles
| Book format | Paperback |
| Fiction/nonfiction | Non-Fiction |
| Genre | Computing & Internet |
| Publication date | December, 2023 |
| Pages | 258 |
| Subgenre | Internet |
| Series title | No Series |
| Edition | 1 |
| Publisher | Packt Publishing |
| Original languages | English |
| Language | English |
| Edu focus | Engineering |
| Is collectible | N |
| Digital file format | |
| Digital reader format | |
| Digital audio file format | |
| Recording time | 0 min |
| Retail packaging | Single Piece |
| Assembled product dimensions (l x w x h) | 7.50 x 0.54 x 9.25 in (19.1 x 1.4 x 23.5 cm) |
| Assembled product weight | 0.99 lb (450 grams) |
| Bisac subject heading | Computers |
من يجب أن يشتري؟

-
Security Professionals
Ideal for security experts looking to enhance their knowledge on integrating SAST and DAST in security protocols.
-
DevOps Teams
Perfect for DevOps teams wanting to adopt DevSecOps practices to improve application security in their development processes.
-
Software Developers
Beneficial for developers aiming to learn secure coding practices and application security testing methodologies effectively.

-
Beginners in Security
Not suitable for those with no prior knowledge of DevSecOps or application security concepts, as it may be complex.
وصف المنتج
هل لديك أي استفسار؟ تحدث معنا
أسئلة العملاء & الإجابات
-
سؤال:
كيف تتسوق Implementing DevSecOps Practices: Understand عبر الانترنت من يوباى?
إجابه: من السهل التسوق في Implementing DevSecOps Practices: Understand عبر الإنترنت من يوباي. كل ما عليك فعله هو البحث عن المنتج واختيار طريقة الشحن الخاصة بك أثناء الدفع وسيتم توصيله الى عنوانك -
سؤال:
هل Implementing DevSecOps Practices: Understand متوفر للتسوق عبر الإنترنت في Iraq؟
إجابه: نعم ، في يوباي Iraq هذا المنتج متاح لك للتسوق بسعر مناسب. Implementing DevSecOps Practices: Understand غير متوفر محليًا ولكن يمكنك الوثوق بنا بخدماتنا للشحن السريع. -
سؤال:
كم من الوقت يستغرق الحصول على المنتج بعد تقديم الطلب؟
إجابه: يختلف وقت تسليم المنتج الذي طلبته حسب ما طلبته وطريقة الشحن التي اخترتها. يتم ذكر وقت التسليم المقدر أثناء عملية الدفع ، لذا كن مرتاحًا أثناء التسوق.
Vandana Verma Sehgal All Books Editorial Review
Implementing DevSecOps Practices: Understand application security testing and secure coding by integrating SAST and DAST is a comprehensive guide designed for professionals in computing and internet fields. This non-fiction paperback spans 258 pages and was published by Packt Publishing in December 2023. The book delves into crucial topics of application security testing, offering insights into both Static Application Security Testing (SAST) and Dynamic Application Security Testing (DAST), making it a valuable resource for engineers. Readers will appreciate its practical approach to integrating security into the software development lifecycle, providing actionable strategies to enhance application security.
مراجعات العملاء وتقييماتهم
1 تقييمات العملاء
-
5 نجمة
100%
-
4 نجمة
0%
-
3 نجمة
0%
-
2 نجمة
0%
-
1 نجمة
0%
أضف تقييم لهذا المنتج
شارك أفكارك مع عملاء آخرين
إيجابيات
- Detailed exploration of application security testing
- Integrates SAST and DAST effectively
- Ideal for engineering professionals
- Published by reputable Packt Publishing
- Practical insights for secure coding practices
سلبيات
- May have limited appeal to non-technical readers
تاريخ سعر المنتج
معلومات مهمة
- القيود: بالنسبة للمنتجات التي يتم شحنها دولياً، يُرجى ملاحظة أن أي ضمان من الشركة المصنعة قد لا يكون صالحاً؛ قد لا تتوفر خيارات خدمة الشركة المصنعة؛ قد لا تكون أدلة المنتج والتعليمات وتحذيرات السلامة مكتوبة بلغة بلد المقصد؛ قد لا يتم تصميم المنتجات (والمواد المصاحبة لها) وفقاً لمعايير بلد الوجهة والمواصفات ومتطلبات الملصقات؛ وقد لا تتوافق المنتجات مع الجهد الكهربي المستخدم في بلد الوجهة والمعايير الكهربائية الأخرى (تتطلب استخدام محوّل كهربي أو جهاز تحويل إذا كان ذلك مناسباً). المستلم مسؤول عن ضمان إمكانية استيراد المنتج بشكل قانوني إلى بلد الوجهة. عند الطلب من يوباي أو الشركات التابعة لها، يكون المستلم هو المستورد المسجل ويجب أن يلتزم بجميع القوانين واللوائح الخاصة ببلد الوجهة.
- ليست كل المنتجات المدرجة على يوباي معروضة للبيع، لأن يوباي هو محرك بحث عالمي. المنتجات تخضع للوائح التصدير / التجارة.
IQD 75892
اطلب الآن واحصل عليه حول الأربعاء, أكتوبر 21
هذا المنتج غير ممنوع في بلدي. (الرجاء الضغط على الرابط أعلاه إذا لم يكن هذا المنتج ممنوعاً في بلدك ، لذلك سيقوم فريقنا بمراجعته والسماح به.)
كمية:
بقي1 عنصر فقط في المخزن.
معاملة آمنة
نوفر لك مدفوعات مشفّرة، وحماية متكاملة للمشتري، مع الالتزام بمعايير PCI DSS وشهادة ISO 27001:2022 لضمان أعلى مستويات الأمان في كل عملية شراء.
أفضل شركائنا اللوجستيين
أسرع توصيل عبر الحدود
المميزات والفوائد
- Integrate security into every stage of development.
- Understand and implement effective application security testing.
- Master secure coding with SAST and DAST tools.
- Learn to maintain a resilient operational environment.
- Adopt automation and compliance for continuous security.
- Suitable for professionals in DevSecOps, application security, and software development.
ضمان Ubuy
تسوّق بثقة مع منتجات أصلية %100، ومدفوعات آمنة متوافقة مع معيار PCI DSS، وحماية بيانات معتمدة وفق ISO 27001، وشحن دولي سريع، وإرجاع مجاني*، وتغليف آمن لكل طلب.